Past event — This event ended 8 days ago.
SOC audits Meetup@Blr
About the event
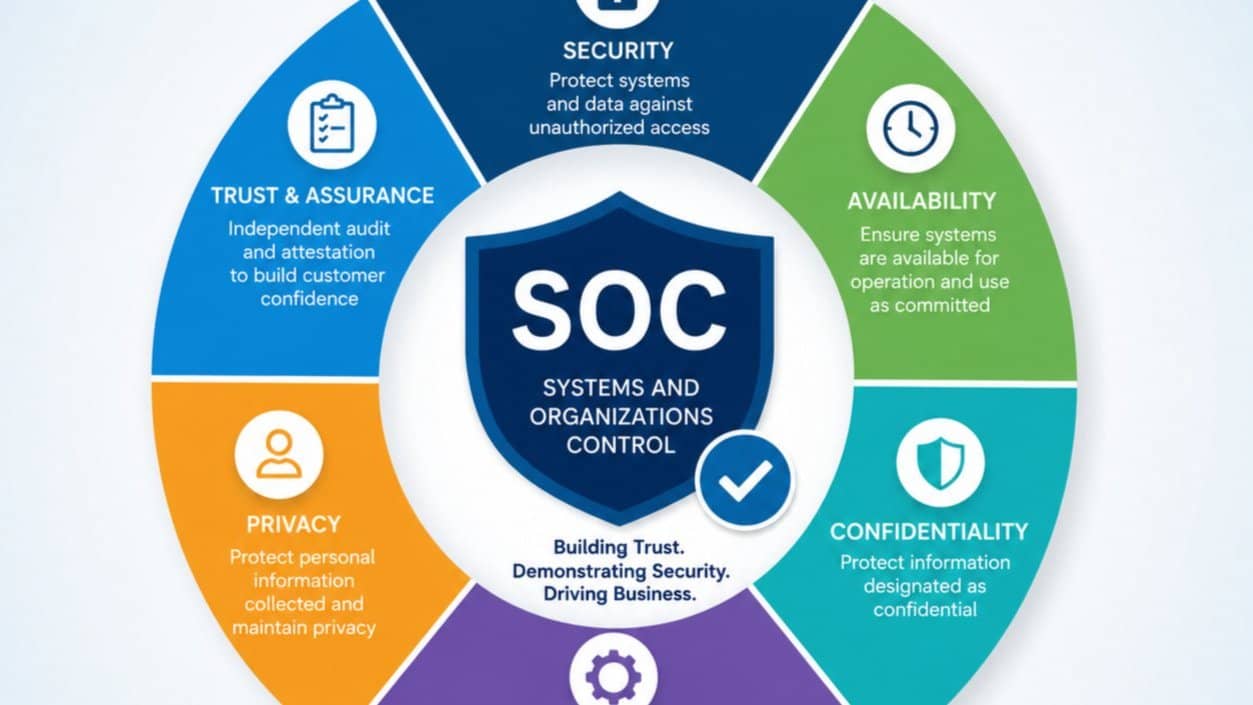
Target Audience: Target Audience • CEOs, CIOs, CTOs, CISOs, and senior leaders responsible for security, compliance, and customer trust • IT Security and Cybersecurity Leaders managing organizational risk and control frameworks • Compliance, Risk, and Governance Decision Makers overseeing audit readiness and regulatory requirements • Engineering and Infrastructure Leaders responsible for secure systems, cloud, and operational controls • DevOps, Platform, and Cloud Leaders managing access, monitoring, and incident response practices • Legal, Privacy, and Data Protection Leaders focused on customer data handling and contractual obligations • PMO and Transformation Leaders driving enterprise compliance programs • Vendor Risk and Third-Party Management Leaders responsible for supplier assurance • Founders and Business Leaders of SaaS, FinTech, HealthTech, and technology-enabled companies seeking enterprise customer trust • Quality, Internal Audit, and Operational Excellence Leaders preparing for SOC readiness and attestation • Procurement and Enterprise Sales Leaders supporting customer security due diligence and large enterprise deals • Companies planning for SOC 2 Type I or Type II attestation to meet client and market expectations TOpics: Overview of SOC frameworks, SOC 1, SOC 2, and SOC 3, and selecting the right path for business needs • Understanding SOC 2 Trust Services Criteria, Security, Availability, Confidentiality, Processing Integrity, and Privacy • Readiness assessment and gap analysis before starting the SOC journey • Building a compliance roadmap, ownership, timelines, and governance structure • Security controls, policies, and evidence requirements for audit readiness • Aligning SOC with existing frameworks such as ISO 27001, NIST, CMMI, and internal controls • Preparing for Type I vs Type II assessments and choosing the right audit scope • Common challenges companies face during SOC implementation and audit preparation • Tools and automation for compliance tracking, evidence collection, and continuous monitoring • Vendor risk management, access controls, incident response, and data protection expectations • Business benefits of SOC certification, customer trust, enterprise sales enablement, and risk reduction • Open discussion with auditors, compliance leaders, and organizations preparing for SOC attestation